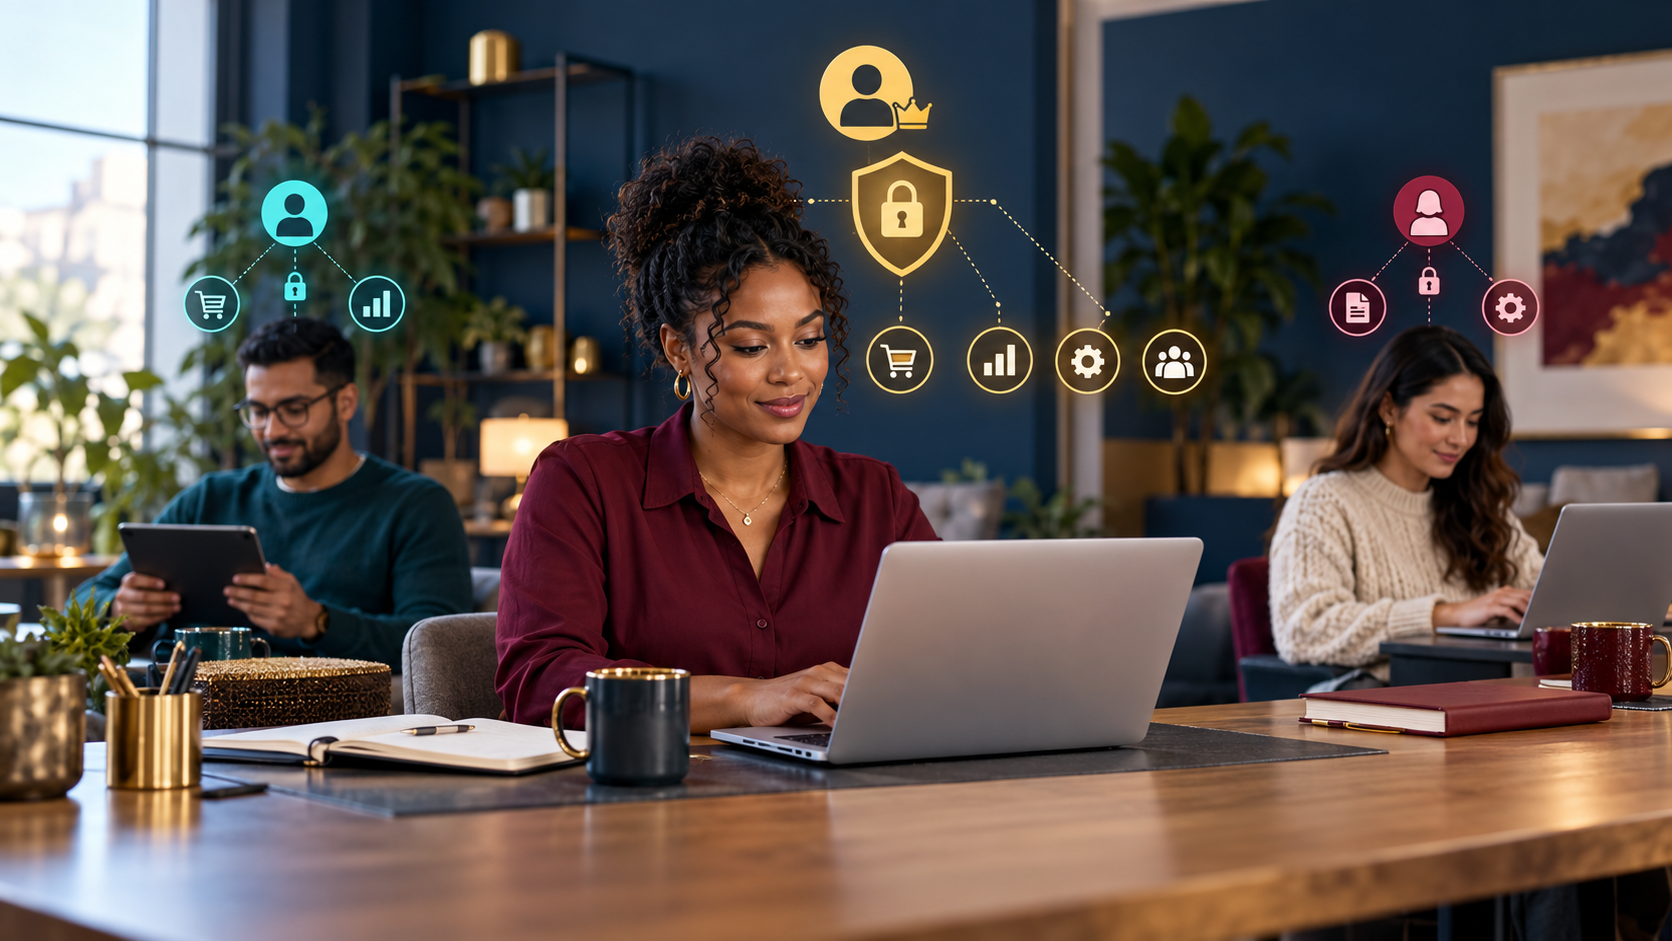
A helper needs to update three product descriptions, so you send them the shop password. A social-media assistant needs to answer comments, so the same login moves into another message. Months later, nobody is certain who still has access—or which person changed a price, refunded an order or connected a new application.
Shared passwords feel efficient when a small business is moving quickly. They are actually a hidden operating cost. They blur responsibility, widen the impact of one compromised device and make offboarding far harder than it should be. A safer system gives each person their own account and only the permissions needed for their work.
The owner login is not a team tool
Your owner or primary administrator account can usually change billing, add other administrators, connect payment services, export customer data and sometimes close the business account. That power is useful precisely because it is exceptional. Treating it as the everyday login for assistants, freelancers and agencies turns one credential into a master key.
The UK National Cyber Security Centre advises organisations to create a separate account for each person because shared accounts make it harder to keep information private, attribute actions and limit the damage from an attack. Its guidance also recommends protecting administrator accounts and revoking access when someone leaves or changes role.
The principle is straightforward: identity first, permission second. You should be able to answer two questions for every meaningful action: who did it? and were they meant to be able to do it?
Start with the task, not the job title
“Assistant”, “manager” and “developer” are broad labels. Permissions should follow the work a person must complete, not the prestige of their title or how much you trust them personally.
- Product editor: create and update listings, images and descriptions, but not payouts or account ownership.
- Customer-support worker: view orders and communicate with customers, but not export the complete customer database.
- Fulfilment worker: see the order information needed to dispatch goods, but not marketing, billing or integrations.
- Marketing specialist: manage campaigns and approved channels, but not refunds, tax settings or shop ownership.
- Bookkeeper: access reports and transactions needed for reconciliation, but not product publishing or user management.
This is least privilege: each person receives the minimum access required for a legitimate task. The NCSC recommends applying this principle to software-as-a-service accounts because it reduces the consequences of compromise or misuse. “Minimum” does not mean making work impossible. It means widening access deliberately when evidence shows it is needed.
Before inviting the next helper: write down the three actions they must perform. Give them access to those actions—not to the whole business.
Build a simple access register
You do not need expensive governance software to begin. A small business can use a controlled spreadsheet or internal document that records:
- the service or platform;
- the person’s name and individual account email;
- their assigned role or permission set;
- the business reason for access;
- who approved it and when;
- the last review date;
- the expected end date for temporary access.
Do not place passwords, backup codes or secret keys in this register. It is a map of authorised access, not a vault. Keep credentials in the platform’s invitation system, a reputable credential manager or another purpose-built secure method.
The register reveals forgotten risk. You may discover a former freelancer who still has an administrator role, a dormant integration with broad permissions, or a personal email address controlling a critical business asset.
Separate everyday work from administration
Even the business owner should avoid using the highest-privilege account for routine browsing, email and content updates when the service supports separation. Keep one protected owner or administrator identity for tasks such as billing changes, new-user approval and security settings. Use a lower-privilege account for daily work.
This reduces exposure. If a malicious link or unsafe browser session compromises the everyday account, the attacker should not automatically inherit the ability to change ownership or disable every other user. The NCSC’s identity and access guidance recommends separate accounts for ordinary work and activities requiring administrative privileges.
Protect each account independently
Individual accounts only help if they are secured properly. Where available, the NCSC recommends passkeys because they are resistant to phishing and cannot be reused like passwords. If a service does not support passkeys, use a strong, unique password and turn on two-step verification.
- Never reuse the shop password for email, social media or another marketplace.
- Protect the primary business email especially carefully because it can reset other accounts.
- Keep recovery details current and under business control.
- Store one-time backup codes safely; do not paste them into team chat.
- Review connected applications and remove those that are no longer used.
Read the NCSC’s current guidance on securing important online accounts and using passkeys for the available choices and their trade-offs.
Use a clean onboarding sequence
Access should begin with a documented invitation, not a password sent through a message.
- Confirm the person’s identity and the work they are engaged to perform.
- Create or invite their individual account using a business-appropriate email address.
- Choose the narrowest role that covers the task.
- Require the platform’s strongest practical sign-in protection.
- Record the access, approver and review date.
- Ask the person to demonstrate the required task without exposing credentials.
That final check matters. Permission labels can be vague, and a role that sounds limited may still expose customer exports or financial information. Test what the user can actually see and change.
Offboarding is a security task, not an awkward conversation
When a contract ends, remove access promptly and record the action. Do not rely on the person promising to forget a password. If a shared password was ever used, change it and review active sessions, recovery details, integrations and administrator lists.
A practical exit sequence is:
- suspend or remove the person’s account;
- transfer ownership of necessary files, campaigns and automations;
- revoke sessions, tokens and connected applications issued for their work;
- check whether they added any new users or recovery methods;
- confirm that the business still has at least one protected owner account;
- update the access register and preserve relevant audit records.
Role changes deserve the same attention. A worker moving from fulfilment to marketing may need different permissions; leaving both sets in place creates “access creep”, where privileges accumulate without a continuing reason.
Run a monthly ten-minute access review
Open the user, administrator and connected-app pages for your most important services. Compare them with the access register. For each person or integration, ask:
- Do we recognise this identity?
- Is the business reason still active?
- Could the role be reduced?
- Is strong sign-in protection enabled?
- Does temporary access now need an end date?
Review email, domain registration, marketplace administration, payment processing, cloud storage and social channels first. These systems can unlock or damage much of the rest of the business.
Why the psychology matters
Shared logins survive because the immediate reward is visible: the helper starts work quickly. The delayed cost is invisible until a mistake, dispute or breach occurs. Good access design changes that default. Invitations, predefined roles and an offboarding checklist make the safer action easier to repeat.
Clear permissions also protect working relationships. An audit trail reduces suspicion because the business does not have to guess who changed what. A contractor can complete the agreed task without carrying responsibility for parts of the operation they were never meant to control.
The safer default for a growing shop
One person, one account. One task, the minimum necessary permission. One owner login, protected and rarely used. Then review and remove access as the team changes.
For further checks on how tools handle sensitive business information, use MaryChuks.com’s 15-minute security audit before sharing client data with an AI tool, or explore more practical guidance in the Security category.
Action for today: replace one shared shop login with individual invitations, reduce each role to the work actually required, and set a date to review access again.
Discover more from Marychuks.com AI, Psychology, Business & CreativeVerse
Subscribe to get the latest posts sent to your email.
One thought on “Never Share Your Shop Password: Give Every Team Member Their Own Access”