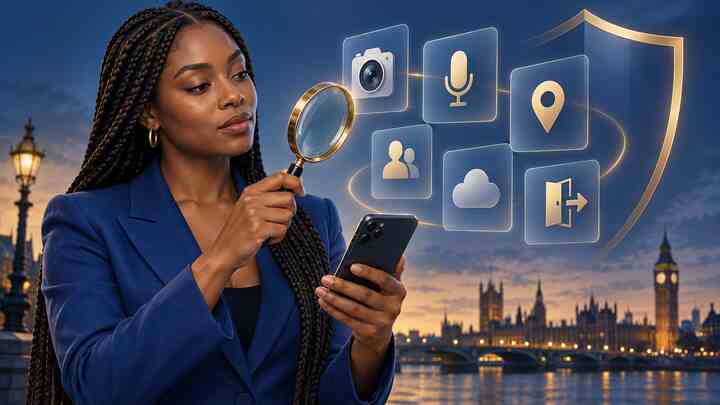
An app installation can look like a tiny decision: tap a button, wait a few seconds, open the icon. In reality, it can begin a much larger relationship involving your location, photographs, microphone, contacts, identifiers and account history.
The useful question is not simply, “Is this app safe?” No store label can answer that with certainty. A better question is: Does the access this app requests make sense for the job I want it to do, and can I control the relationship afterwards?
This five-minute audit turns that question into a repeatable routine. It is not a guarantee against fraud or poor security. It is a practical way to notice avoidable risk before convenience turns into commitment.
Minute one: confirm who is behind the app
Begin with the developer, not the star rating. Check the developer name, linked website, support address and recent update history. Similar names and familiar-looking logos are not proof of identity. If the app claims to represent a bank, public body, retailer or well-known service, reach its store listing from that organisation’s official website rather than relying on a search result or an advert.
A credible listing is not the same as a trustworthy product, but contradictions matter. A broken privacy-policy link, an unrelated developer website, no usable support route or an unexplained publisher name should slow you down. For an app handling money, health information, passwords, identity documents or children’s data, uncertainty is a reason to stop rather than experiment.
Minute two: match each permission to a real feature
Permissions should be proportionate to the service. A document scanner may need the camera when you scan a page. A navigation app may need location while you use it. Those explanations do not automatically justify permanent background access, your full contact list or every photograph on the device.
- Camera and microphone: Which named feature uses them, and can access be limited to the moment you activate that feature?
- Location: Would approximate or “while using” access work instead of precise, continuous tracking?
- Photos and files: Can you select individual items rather than expose the whole library?
- Contacts: Is contact discovery central to your purpose, or merely convenient for the company?
- Notifications: Do you need urgent alerts, or is the request mainly an invitation to increase engagement?
A mismatch is a signal to investigate, not proof that an app is malicious. Some legitimate functions rely on permissions in ways that are not obvious. The developer should nevertheless be able to explain the connection clearly.
Minute three: read privacy disclosures without treating them as certification
Store disclosures are valuable because they create a common place to compare products. They are not independent security audits.
Google explains that the Play Store’s Data safety section is supplied by developers and may vary according to the way an app is used, a user’s region and age. It also distinguishes the disclosure from the technical permission list: data can be processed on the device, collected through systems that do not require a listed permission, or handled differently in different circumstances. See Google’s official explanation of Data safety information.
Apple likewise requires developers to provide privacy details for App Store listings. Use the label to ask three separate questions: what data may be collected, whether it may be linked to you, and whether it may be used to track you across other companies’ apps or websites. Then compare those answers with the privacy policy and the product’s actual purpose.
Pay special attention to broad categories such as identifiers, purchases, precise location, health data and “other data”. A long list is not automatically unacceptable—a complex service may genuinely need more information—but the benefit and the cost should be legible before installation.
Minute four: find the exit before creating an account
Uninstalling software does not normally delete the account or information already held by the provider. Before registering, locate the account-deletion route and read what the company says it will erase, retain or anonymise.
Google Play policy requires apps that let users create accounts to provide an in-app path to request deletion and a web link for deletion requests. That is useful, but it does not mean every item disappears immediately: some records may be retained for security, fraud prevention or legal obligations. The important point is that the route and the exceptions should be understandable before you hand over sensitive information.
Also check whether you can export important material, cancel a paid subscription separately and revoke any “Sign in with…” connection. Account deletion, subscription cancellation, cloud-file deletion and removal of a third-party login connection are related but different actions.
Minute five: start with the narrowest access and observe
If the app passes the first four checks, install it with optional permissions denied. Grant access when a feature clearly needs it, choose limited or one-time options where available, and review background activity and notifications after a few days.
On supported iPhones and iPads, Apple’s App Privacy Report can show how often apps accessed location, photos, the camera, microphone and contacts during the previous seven days, as well as network activity and frequently contacted domains. Reporting begins after the feature is enabled, and Apple says the report is stored on the device. Access shown in the report is evidence that a permission was used; it is not, by itself, proof that the developer collected or misused the information.
Android users can review and change permissions by app or permission type, and can configure unused-app handling on supported devices. Google’s current instructions are available in its guide to changing app permissions.
Raise the standard when the consequences are higher
Not every installation deserves the same investigation. A simple offline timer and a financial app do not create equal exposure. Apply a stricter threshold to products that handle:
- banking, payments, investments or credit;
- passwords, authentication codes or virtual private networks;
- medical, fertility, mental-health or biometric information;
- children’s accounts, school records or family location;
- identity documents or intimate photographs;
- door locks, cameras and other smart-home controls.
For these categories, verify the provider through an independent official channel, enable multi-factor authentication where appropriate, and avoid installing from links delivered through unexpected messages.
Red flags that deserve a pause
- The app demands unrelated access before showing any useful feature.
- The privacy policy is missing, broken, copied vaguely or names a different product.
- The developer identity cannot be reconciled with the organisation the app claims to represent.
- Account deletion is hidden, circular or described only as uninstalling the app.
- You are pressured to install outside the normal store without a clear, verifiable reason.
- A sign-in screen asks for credentials in a context you cannot authenticate.
- Urgency, prizes or fear are used to prevent you from checking details.
The evidence is useful; judgement still matters
A permission list is technical evidence of what the software may request. A store disclosure is the developer’s account of data practices. A privacy report can record recent access and network activity. None of these alone proves intent, security quality or future behaviour.
The practical interpretation is cumulative. A known developer, a coherent purpose, narrow permissions, clear disclosures, an accessible deletion route and observable behaviour reinforce one another. Several mismatches do the opposite. You do not need courtroom certainty to decide that an optional app is not worth the exposure.
A one-minute checklist to keep
- Is this the real developer and official listing?
- Can I explain every sensitive permission in one sentence?
- Do the store disclosure and privacy policy agree with the product’s purpose?
- Can I find a genuine account-deletion route?
- Can I begin with limited access and review what happens afterwards?
Repeat the audit every few months for apps you keep. Remove unused software, revisit permissions, disconnect old third-party account links and check subscriptions separately. Google also provides a central guide for reviewing connections between a Google Account and third-party apps.
The goal is not to fear every permission. It is to make access intentional. Five careful minutes before installation can prevent a much longer clean-up later.
Featured image: conceptual AI-generated illustration; not documentary evidence.
Discover more from Marychuks.com AI, Psychology, Business & CreativeVerse
Subscribe to get the latest posts sent to your email.