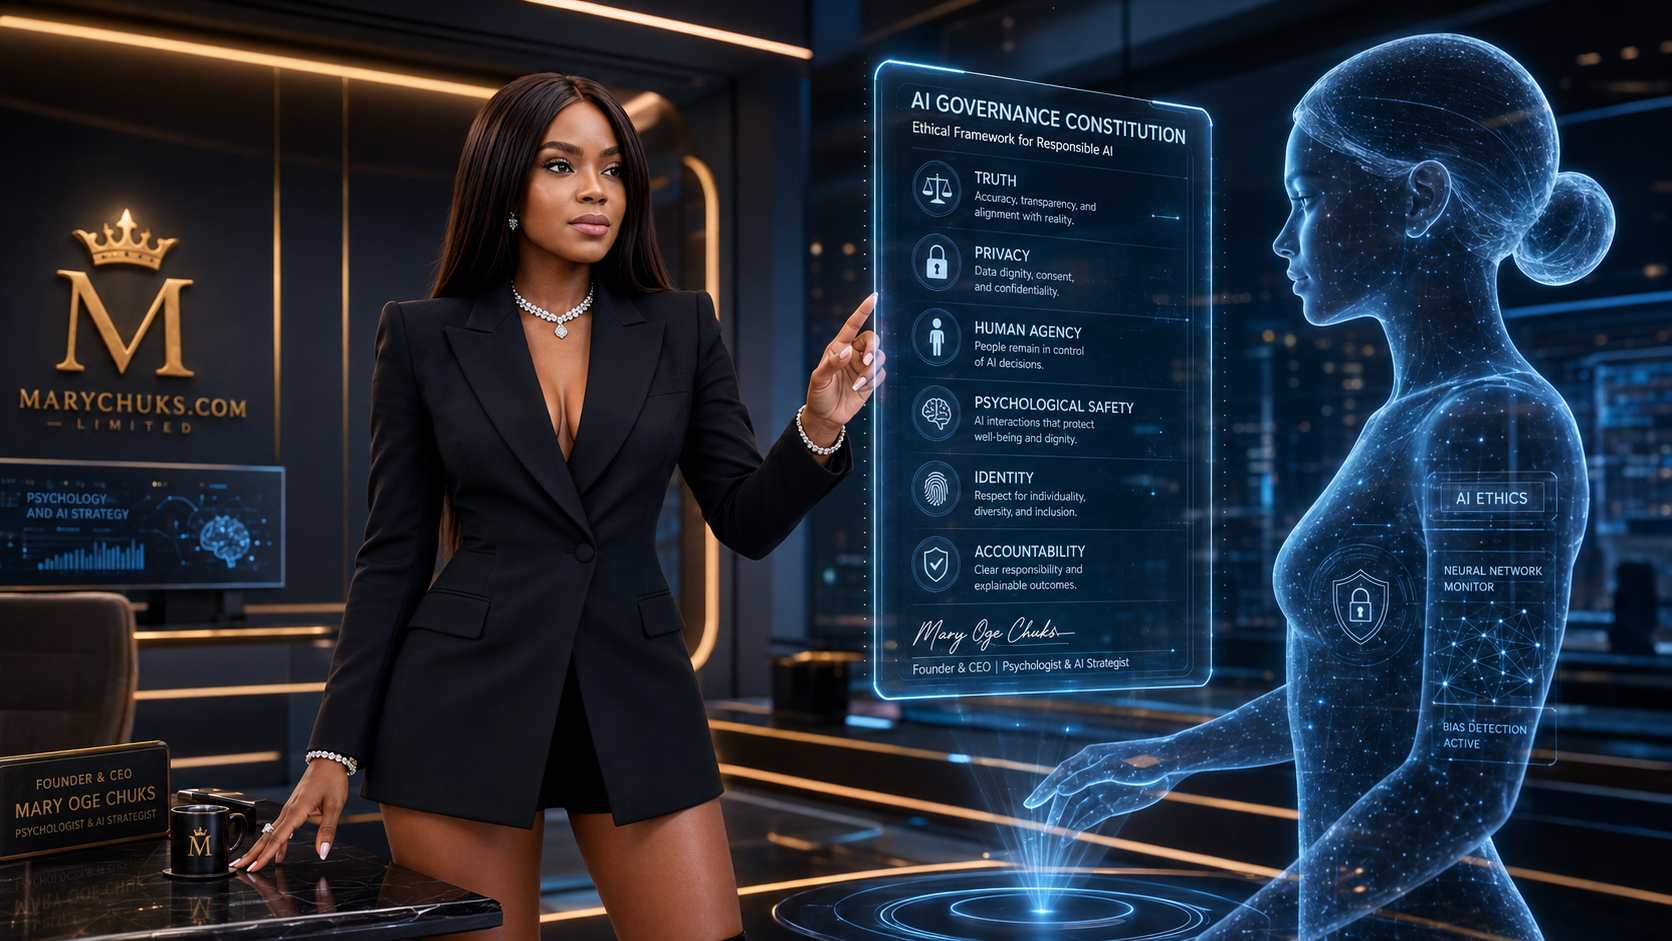
AI governance can sound like something only large corporations need.
It is not.
A small company may already have employees placing customer information into AI tools, generating marketing claims, summarising contracts, or automating important workflows.
The organisation, therefore, needs a simple answer to an important question:
What are our rules for using AI?
Governance Does Not Need to Begin With a Huge Manual
A small business can start with a short policy.
The purpose is not to create bureaucracy.
It is to make expectations clear.
A practical AI-use policy should address several areas.
1. Define Approved Uses
Explain what employees may use AI for.
Examples might include:
brainstorming;
drafting non-sensitive content;
summarising public information;
administrative support;
coding assistance;
and internal idea generation.
This gives people useful freedom.
2. Define Restricted Uses
Certain activities deserve additional review.
These may include:
uploading personal customer data;
sharing confidential company information;
making employment decisions;
giving professional advice;
creating financial representations;
or allowing AI to take significant actions automatically.
The organisation should identify which uses require permission.
3. Create a Data Rule
Employees should know what information they can enter into an AI system.
A straightforward rule might be:
Do not upload confidential, personally identifiable, or commercially sensitive information unless the tool and workflow have been specifically approved for that purpose.
This single principle can prevent significant problems.
4. Require Human Review
AI-generated work should not automatically become published work.
Humans should review outputs where accuracy, reputation, safety, or customer experience matters.
Review should check:
facts;
tone;
confidential information;
bias;
unsupported claims;
and whether the output actually answers the intended question.
5. Keep an Approved Tool List
Without guidance, employees may create accounts with dozens of different AI products.
That makes data management difficult.
Maintain a simple approved-tool list.
Record:
the tool;
its purpose;
who can use it;
which type of data it may process;
and who owns the account.
6. Assign Responsibility
Someone should own the policy.
In a small company, this may be the founder, operations manager, technical lead, or another responsible person.
Employees need to know where to ask questions.
Governance fails when responsibility belongs vaguely to “everyone.”
7. Review Important Automated Actions
AI systems may eventually move beyond suggestions and perform actions.
Sending messages.
Updating records.
Creating transactions.
Changing schedules.
Triggering workflows.
The more consequential the action, the more carefully permissions should be designed.
Ask:
What can the system do?
What requires approval?
Can an action be reversed?
Is there an audit trail?
8. Keep the Policy Alive
AI changes quickly.
A policy written once and forgotten will eventually become irrelevant.
Review it periodically.
Which tools are people actually using?
Have new risks appeared?
Are employees confused about anything?
Has the business introduced new automated workflows?
Governance should evolve with practice.
Responsible AI Can Be Practical
Small businesses do not need to choose between innovation and responsibility.
Clear rules can make experimentation easier because people understand the boundaries.
Use AI.
Test new workflows.
Improve productivity.
But know where information goes, who remains accountable, and when a human needs to intervene.
That is the beginning of useful AI governance.
Discover more from Marychuks.com AI, Psychology, Business & CreativeVerse
Subscribe to get the latest posts sent to your email.